TryHackMe 5 Minute Hacks - The Game Writeup
Abstract
I’ve decided to start creating writeups for every single challenge in TryHackMe, so I got myself a subscription this week. This is the first in a series of hundreds of writeup articles from TryHackMe.
I hope it is benefitial and fun to you, as it was for me to beat this challenge, and that I can offer something you can learn more.
The Challenge - The Game
 | Level: Easy Time: 10 min Type: Forensics Requirements: Almost zero, maybe a bit of Linux and simple file manipulation commands knowledge. Resources Used: - Kali Linux - strings command. |
|---|
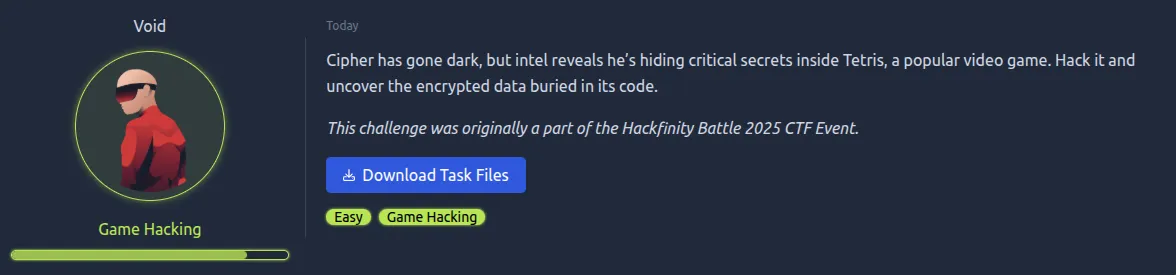
Walkthrough
This challenge is very simple, judging by the its instructions. All that is required is to find a flag inside a tetris game file.
Once the challenge zip file is downloaded and opened, inside it contains a simple ‘Tetrix.exe’ executable, you need to uncompress.
The very first thing we generally do in challenges like that is to check for any readable strings inside the given file:
strings Tetrix.exeThe result list is too long so let’s try to be more specific about it and filter by the flag naming convention ‘THM{STRING}’
strings Tetrix.exe | grep -i 'thm{'And Voilá, there we have it!
Related Posts
- [TryHackMe 5 Min Challenges](/blog/Writeups/challenges